Who shows up
Steadfast was founded on a simple thesis: security posture should carry diligence and accelerate exits, not just survive them. Trust is a revenue asset and we build it like one.
Our mission
The best security programs are mostly invisible. Engineers ship, sales closes and the audit happens on schedule because someone owns the work. We build programs that run on confidence, not fear.
That takes clarity over complexity and collaboration over transactions. We speak the language of CEOs and CISOs. We bring experience from the CISO, auditor, GRC and AI security side of the table and stay engaged until security is part of your culture.
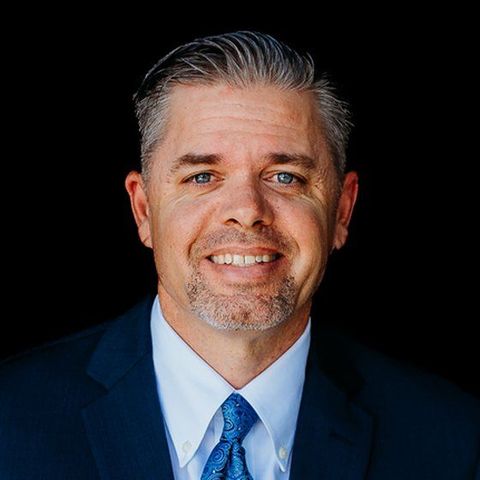
Justin has spent two decades in healthcare and federal security aligning programs with HITRUST, HIPAA, SOC 2, ISO 27001, CMMC and FedRAMP. He has sat on the assessor side of the table, including service on the HITRUST external assessor council, so clients are prepared for how reviewers actually test rather than how the checklist reads.
He gives executives risk in plain terms with a dated plan and a cost, and he mentors up and coming security professionals.
Certifications. CCSFP, CHQP, CMMC Registered Practitioner, ISO 27001, ISO 27701 and ISO 42001 Lead Auditor. BBA in Computer Information Systems, Texas State University.
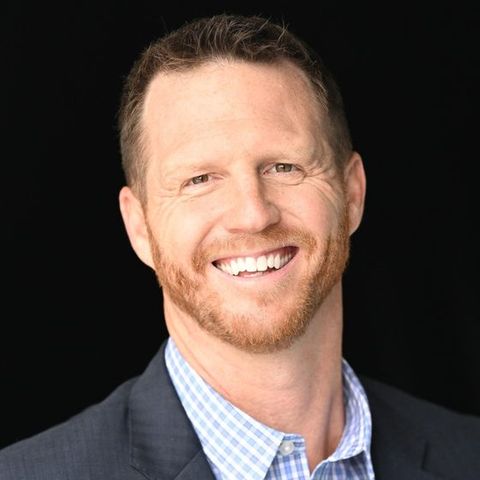
Marc leads partners, business development and operations at Steadfast. He started as one of the original SOX auditors at PwC and has spent two decades since in cybersecurity advisory and sales leadership, including six consecutive President's Club awards.
He makes sure the audit, the platform and the whole program run as one engagement with one accountable team. His rule is keep it simple and do the right thing.
Background. Marc holds an MBA from Cleveland State University and a BS in Accounting from Ohio University.
Operators, not observers. Talk to a partner, not a sales rep.